 ع

Blockchain analysis firms TRM Labs and Chainalysis attributed a $6.3 billion theft from Binance on October 29 to North Korea’s TraderTraitor hacking group with high confidence, according to their published assessments. The incident, which drained funds from hot wallets across 10 blockchains in roughly 20 minutes, marks the largest cryptocurrency theft recorded and dwarfs the previous high of $1.5 billion taken from Bybit in February 2025. Binance confirmed a security breach that day and immediately suspended withdrawals while it worked with law enforcement and tracing specialists to recover assets.
TRM Labs reported that the attackers compromised a Binance engineer’s laptop, which granted access to a service container used for processing withdrawals. The group then leveraged an Ethereum upgrade known as EIP-7702 to prepare 50 pre-signed authorizations in advance that turned a hot wallet into an automated sweeper under their control. According to the firm’s analysis, this infrastructure compromise allowed simultaneous transfers on multiple chains, with more than $6.36 billion moved before most counterparties could react.
Chainalysis data placed North Korea’s cumulative cryptocurrency thefts at $6.75 billion through the end of 2025, a figure that included the Bybit breach the FBI attributed to the same TraderTraitor unit. The firm noted that proceeds from the latest attack began mixing in real time with funds from a prior Bitget exploit already linked to North Korean actors. Reuters reported that cybersecurity researchers view TraderTraitor as an elite financially focused subunit of the broader Lazarus Group, drawing on experienced operators previously associated with APT38 activities.
Sophos senior director of threat research Rafe Pilling stated that early indicators of the Binance breach aligned closely with North Korea’s established tactics for mapping corporate approval systems and targeting personnel. A SlowMist security operations lead told The New York Post that the group specialises in social engineering by posing as employers or investors to extract credentials rather than exploiting code directly. These methods have allowed North Korean hackers to fund the country’s weapons programmes, according to multiple expert assessments cited by Reuters.
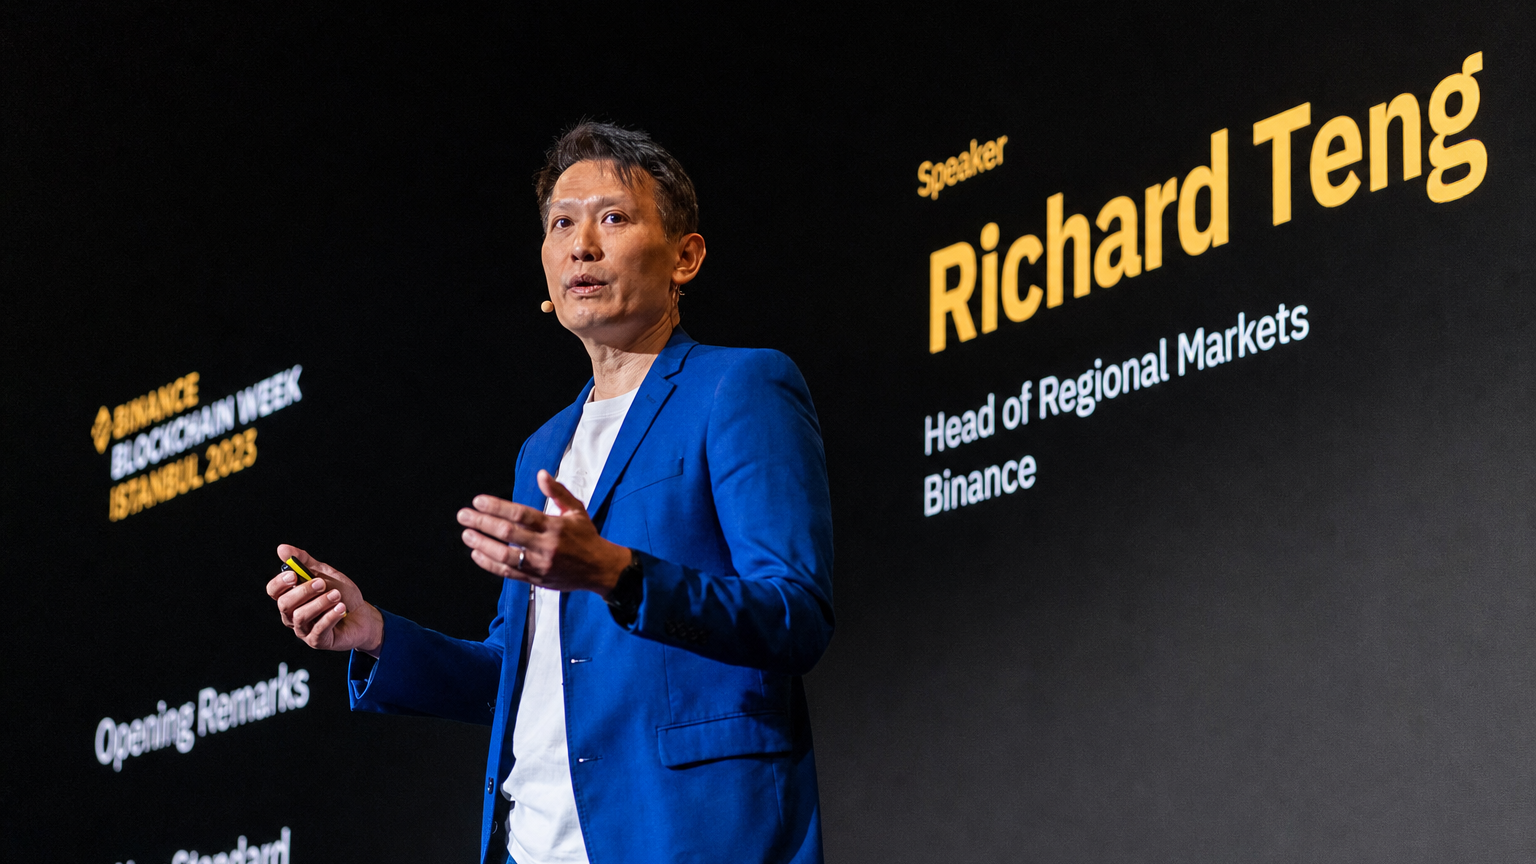
Binance said in a statement that it had located roughly $3 billion of the stolen funds through collaboration with stablecoin issuers and other partners, including freezes by Tether and Circle. Co-CEO Richard Teng announced that the exchange would cover all customer losses from company resources and expected to restore withdrawals within days after completing a full security review. The company later disclosed that its investigation uncovered additional breach points and malware designed to erase forensic traces.
The attack prompted immediate calls from other crypto platforms for enhanced industry information sharing to counter increasingly sophisticated state-backed operations. Elliptic analysts described the heist as almost certainly the single largest known theft of any kind, a characterisation echoed across blockchain intelligence reports. North Korea has consistently denied involvement in cryptocurrency thefts.