 ع

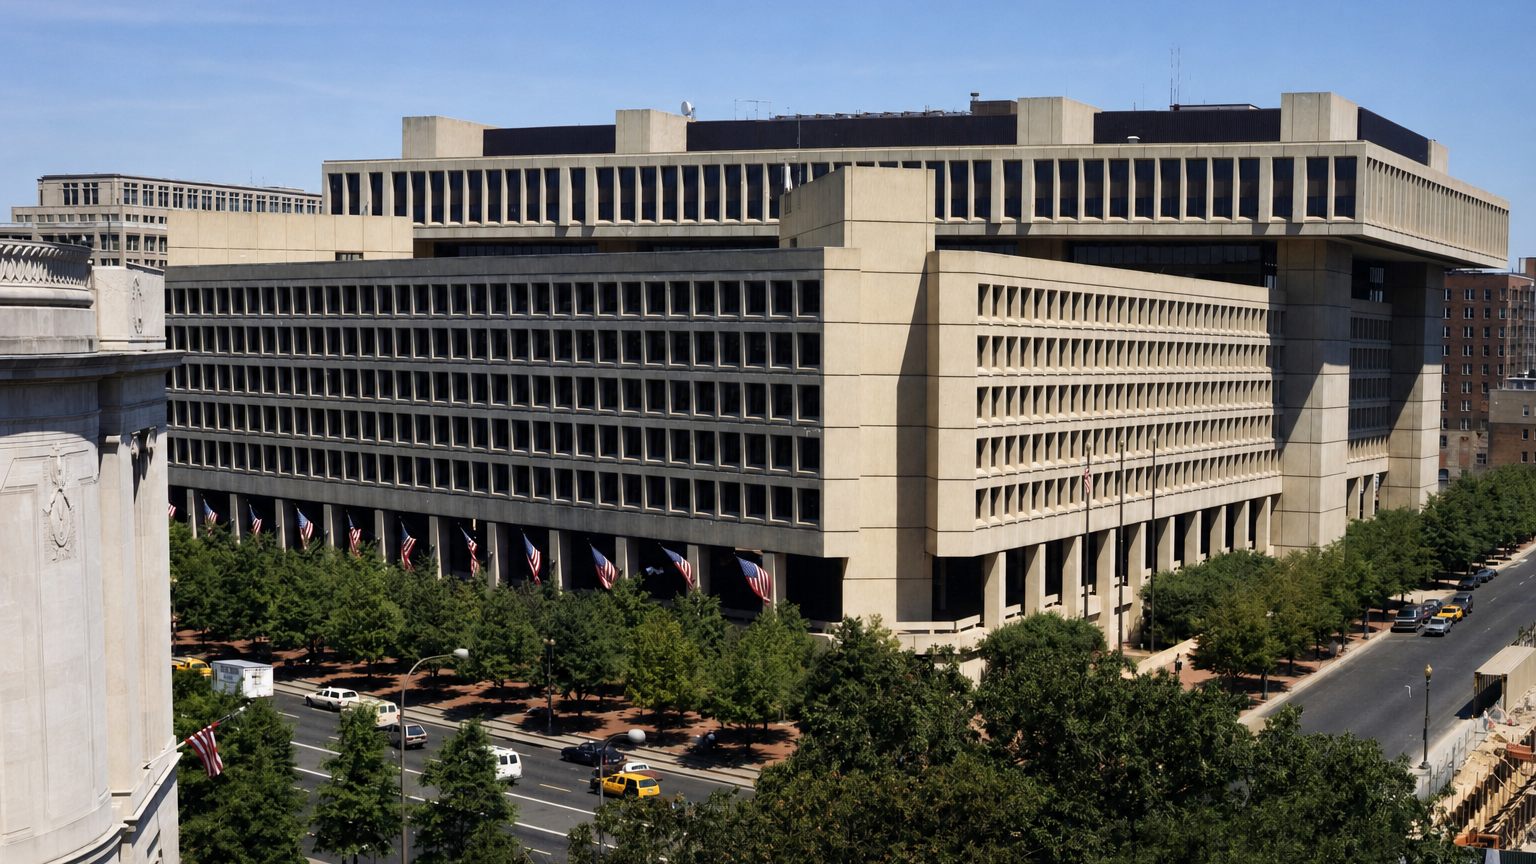
A prolific cybercriminal group known as ShinyHunters asserted it compromised multiple FBI systems including a medical records database called MedLink, according to reports from several outlets that received samples of the allegedly stolen information. The data encompasses full names, home addresses, phone numbers, badge numbers and spouse details for thousands of special agents and job applicants, a New York Times account indicated on September 23. Samples reviewed by journalists contained doctors’ notes on conditions such as high cholesterol and blood in the urine, with the breach traced to a vulnerability in Oracle cloud storage used by the agency. The FBI stated it was actively and aggressively investigating the matter while collaborating with third-party providers supporting its jobs portal.
The hackers posted their claims on a darknet site and contacted media outlets after breaching the systems on September 22, Cybernews reported, adding that the group provided what appeared to be a 5,000-record sample for verification. ShinyHunters described the material as including sensitive personally identifiable information, background checks, educational records and serious medical details in a statement addressed to FBI Director Kash Patel. A Politico report on September 22 cited two people with knowledge of the incident who viewed the claims as credible and a significant counterintelligence concern. The group has not yet publicly released the full dataset, which it says totals between two and three terabytes.
ShinyHunters framed the operation as retaliation for an FBI advisory issued in spring 2026 that warned about the group’s tactics and advised victims against paying ransoms, according to a Technology Org summary of the events. The hackers demanded the bureau retract that warning within seven days, a Nextgov/FCW article from September 22 detailed. Professor Ciaran Martin, former head of the UK’s National Cyber Security Centre, told BBC News the potential exposure ranked as serious as data breaches get if confirmed. Experts cited across reports warned that the information could expose agents to blackmail, scams, impersonation attempts or targeted threats from foreign intelligence services.
The stolen records relate to fitness-for-work examinations and appear to include senior officials such as deputy directors, with some entries matching publicly available FBI employment data, a BBC News assessment found on September 25. The bureau’s online jobs portal and special agent applicant system were temporarily taken offline following the claims, multiple sources confirmed. ShinyHunters asserted access extended beyond human resources to criminal justice information services, though independent confirmation of every compromised system remains incomplete. The FBI has so far declined further public comment beyond its initial statement on the probe.
This incident marks the latest high-profile claim by ShinyHunters, a group previously linked to breaches at other major organizations, according to a Cybernews review of its history. The FBI employs roughly 38,000 people, meaning a full compromise would represent an unprecedented exposure of law enforcement personnel details, one BBC News article noted. Verification efforts by outlets including 404 Media, which first broke the story, involved cross-checking names against external records that aligned in multiple cases. No evidence has emerged that the data has been used for extortion or further distribution as of September 25.
Law enforcement agencies have increased focus on protecting employee data amid rising cyber threats, with the breach highlighting vulnerabilities in cloud-hosted government systems, a Politico analysis stated. The group emphasized in its communications that the attack was not financially driven but aimed at exposing what it called unfair accusations against it. Further details on the exact entry point continue to be examined by investigators working with technology providers.